自分専用の VPN
Nanocl では作業を簡単にするため、すぐに使える VPN の Statefile を用意しています。
@Lin Song の hwdsl2/docker-ipsec-vpn-server を基にしており、Nanocl の公式リポジトリ から利用できます。
nanocl state apply -fs nr.next-hat.com/v0.18/ipsecこの Statefile のマニュアルは、次のコマンドで表示できます。
nanocl state man -s nr.next-hat.com/v0.18/ipsecStatefile Args で設定できる範囲を超えて調整したい場合は、ダウンロードして必要に応じてカスタマイズできます。
wget nr.next-hat.com/v0.18/ipsecVPN の Statefile の内容は次のとおりです。
ApiVersion: v0.18

Args:
- Name: namespace
  Kind: String
- Name: public-ip
  Kind: String
- Name: dns
  Kind: String
  Default: "1.1.1.1"

Namespace: ${{ Args.namespace }}

# See all options:
# https://docs.next-hat.com/references/nanocl/objects/cargo
Cargoes:
- Name: vpn
  PortBindings:
    500/udp:
    - HostPort: "500"
    4500/udp:
    - HostPort: "4500"
  Containers:
  - Name: vpn
    Image: hwdsl2/ipsec-vpn-server:latest
    Env:
    - VPN_PUBLIC_IP=${{ Args.public-ip }}
    - VPN_DNS_SRV1=$$INTERNAL_GATEWAY
    - VPN_DNS_SRV2=${{ Args.dns }}
    - VPN_L2TP_NET=192.168.42.0/16
    - VPN_L2TP_LOCAL=192.168.42.1
    - VPN_L2TP_POOL=192.168.42.10-192.168.42.254
    - VPN_XAUTH_NET=192.168.43.0/16
    - VPN_XAUTH_POOL=192.168.43.10-192.168.83.254
    HostConfig:
      Binds:
      - /opt/vpn:/etc/ipsec.d
      - /lib/modules:/lib/modules
      CapAdd:
      - NET_ADMIN
      Devices:
      - PathOnHost: /dev/ppp
        PathInContainer: /dev/ppp
        CgroupPermissions: rwm
      Sysctls:
        net.ipv4.ip_forward: "1"
        net.ipv4.conf.all.accept_redirects: "0"
        net.ipv4.conf.all.send_redirects: "0"
        net.ipv4.conf.all.rp_filter: "0"
        net.ipv4.conf.default.accept_redirects: "0"
        net.ipv4.conf.default.send_redirects: "0"
        net.ipv4.conf.default.rp_filter: "0"
        net.ipv4.conf.eth0.send_redirects: "0"
        net.ipv4.conf.eth0.rp_filter: "0"
次のように利用できます。
nanocl state apply -fs nr.next-hat.com/v0.18/ipsec -- --namespace private --public-ip $(curl -s http://ipinfo.io/ip)上のファイルでは、VPN 専用の DNS を作成しています。
これにより、ドメインの作成や既存のドメインの上書きを行い、Cargo へ転送できます。
VPN に接続する前に、次のコマンドで認証情報を取得できます。
nanocl cargo -n private logs vpn次のような結果が表示されます。
================================================

IPsec VPN server is now ready for use!

Connect to your new VPN with these details:

Server IP: server-public-ip
IPsec PSK: secret-psk
Username: vpnuser
Password: secret-password
VPN への接続方法はシステムによって異なるため、ここでは説明しません。
コンテナイメージの詳細は、公式ドキュメント で確認できます。
これで任意の名前空間に Cargo を作成し、VPN からアクセスできるようにできます。例は次のとおりです。
ApiVersion: v0.18

Namespace: global

# See all options:
# https://docs.next-hat.com/references/nanocl/objects/cargo
Cargoes:
- Name: deploy-example
  Containers:
  - Name: web
    Image: ghcr.io/next-hat/nanocl-get-started:latest
    Env:
    - APP=GET_STARTED1

# See all options:
# https://docs.next-hat.com/references/nanocl/objects/resource
Resources:
- Name: vpn-dns
  Kind: ncdns.io/rule/v0.10
  Data:
    Entries:
    - Name: my-domain.internal
      IpAddress: Internal

- Name: my-domain.internal
  Kind: ncproxy.io/rule/v0.15
  Data:
    Rules:
    - Domain: my-domain.internal
      Network: Internal
      Locations:
      - Path: /
        Target:
          Key: global.deploy-example.c
          Port: 9000
private 名前空間のゲートウェイを参照する private.nsp を複数の場所で使っています。別の名前空間を使った場合は、変更が必要になることがあります。
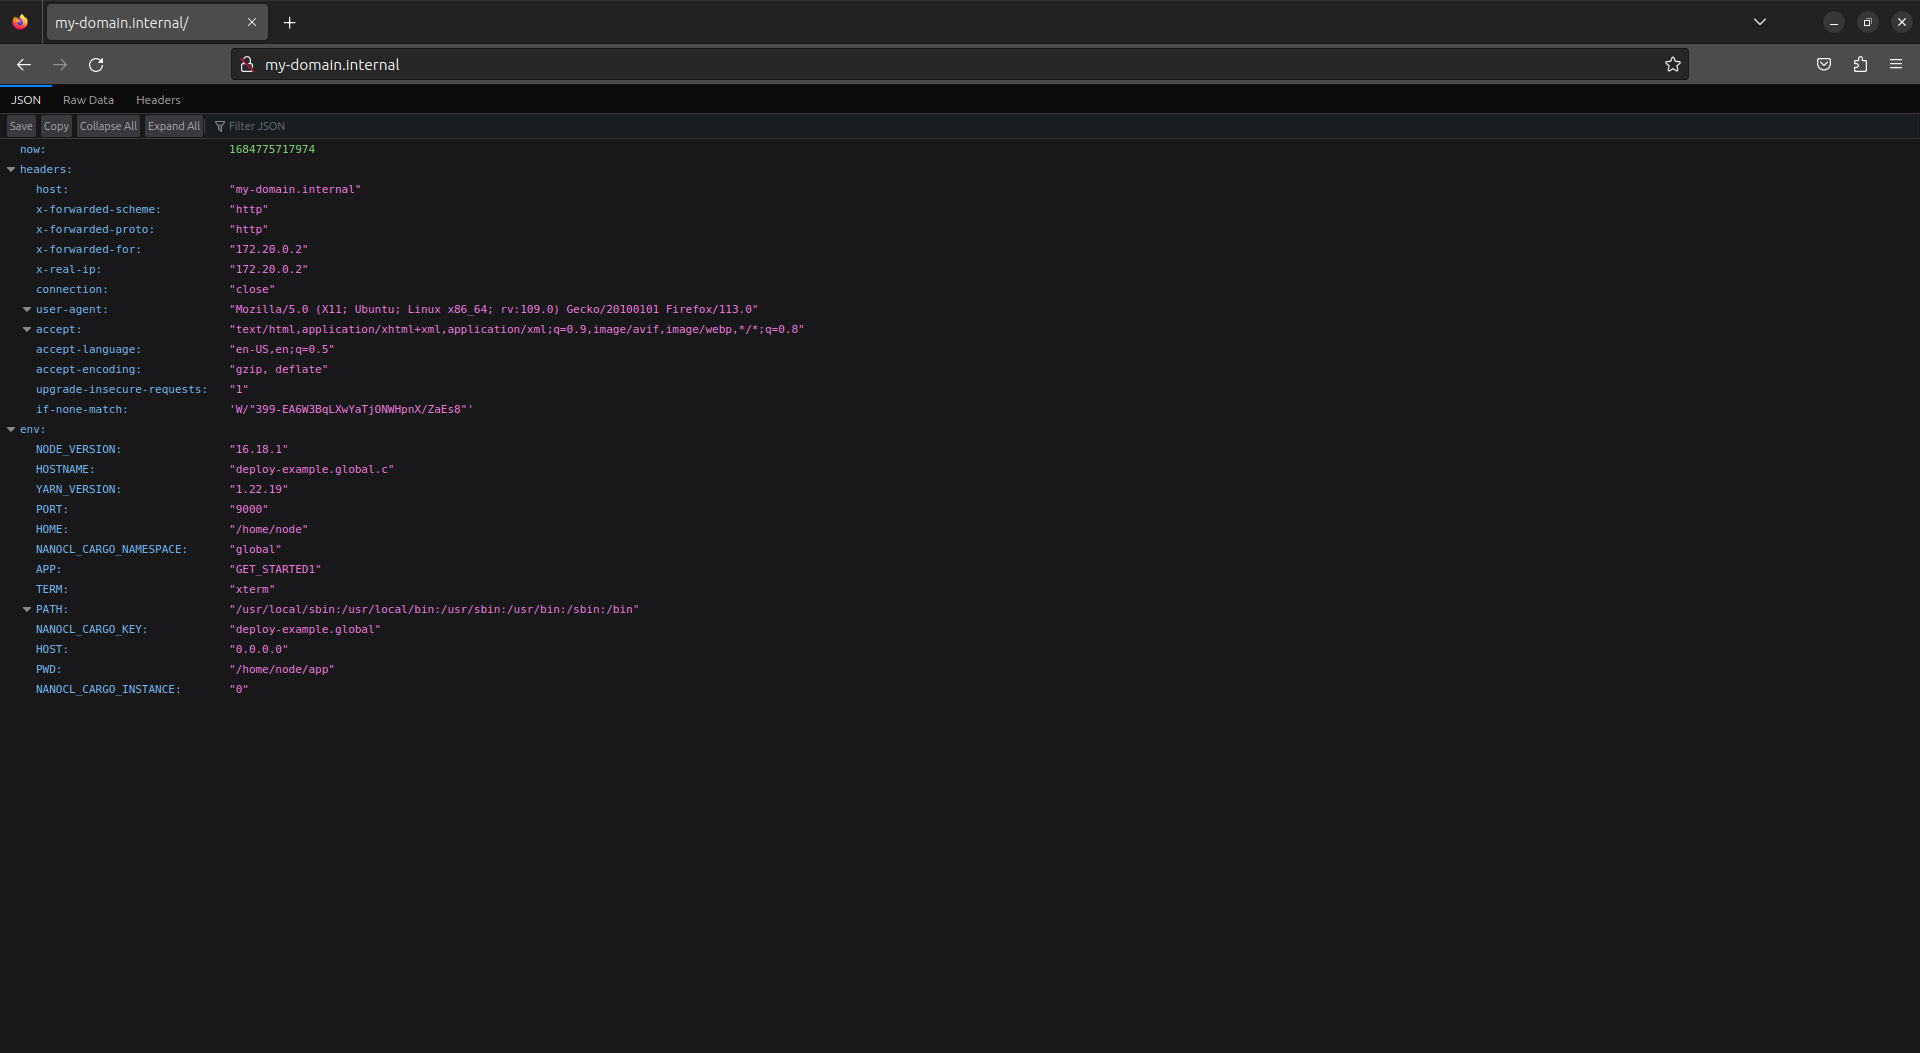
この設定を適用すると、http://my-domain.internal にアクセスできるようになります。
最終更新日